Healthcare Cybersecurity Frameworks: How to Choose and Implement One
Updated 03 Sep 2026
17 Min
3116 Views
Healthcare regulators, such as HIPAA (US), PHIPA and PIPEDA (Canada), GDPR and NIS2 (EU), name the outcome and leave you the controls. None of them hands you a set of controls. Healthcare cybersecurity frameworks fill that gap: they turn regulatory outcomes into concrete controls, assign owners, and produce the evidence an auditor or a partner will ask for.
Cleveroad has built healthcare software since 2011 and works with domain-specific security requirements throughout product development. Based on this practical experience, we created this guide to explain what NIST CSF 2.0, HHS 405(d) HICP, HITRUST CSF, and other healthcare cybersecurity frameworks are designed for, when to use each one, and how to combine them into a single security program.
Key takeaways:
- Pick the framework based on what's driving the work. A partner audit, a regulator finding, and a product launch each point to a different starting framework.
- NIST CSF 2.0 can serve as the core structure for your security program through six functions: Govern, Identify, Protect, Detect, Respond, and Recover.
- HHS 405(d) HICP is the practical entry point for small teams because Technical Volume 1 sizes its safeguards to organizations with limited IT staff.
- HITRUST is the only framework here that buyers can treat as proof, so its higher assessment cost makes sense when a payer or health system requires validated evidence.
- You do not have to choose only one framework. Use NIST CSF to organize the program, HICP to add healthcare-specific practices, CIS Controls as the technical layer, and HITRUST when external assurance becomes a business requirement.
What Is a Healthcare Cybersecurity Framework?
A healthcare cybersecurity framework is a structured set of controls and practices that helps healthcare organizations turn security requirements into concrete actions. HIPAA sets enforceable requirements for protecting patient data but leaves you flexibility in how you meet them. A framework provides the structure to select controls, assess risks, measure security maturity, and document evidence of compliance.
Frameworks also give security, IT, compliance, and executive teams one vocabulary for the same risks, which matters as soon as more than one team owns part of the program. In NIST CSF 2.0, three elements help you adapt the framework to your risks and priorities:
- Framework core. Defines cybersecurity outcomes and groups them into functions, categories, and subcategories that teams can map to controls and responsibilities.
- Implementation tiers. Show how consistently an organization incorporates cybersecurity risk management into its processes, from partial practices to adaptive ones.
- Profiles. Compare your current and target cybersecurity posture so teams can identify gaps and prioritize improvements.
Why Healthcare Organizations Adopt a Cybersecurity Framework
A cybersecurity framework gives you a repeatable way to reduce exposure to breaches and restore critical systems faster. It also creates documented evidence of recognized security practices, which can affect HIPAA enforcement outcomes if an incident still occurs.
Reducing possible breach costs
Healthcare remains the costliest industry for data breaches. IBM's 2026 Cost of a Data Breach Report put the healthcare breach at $6.64 million, the 13th consecutive year healthcare ranked highest among the industries IBM studied, as reported by Becker's Hospital Review. That is down 10.5% from $7.42 million a year earlier, so costs are falling while the ranking holds.
Detection is the slower half. IBM's 2025 edition, the most recent to break out a healthcare figure, put the time to identify and contain a healthcare breach at 279 days, per HIPAA Journal, against a cross-industry mean that reached 247 days in the 2026 report. A framework closes that gap by defining monitoring controls, incident owners, escalation paths, and recovery procedures before an attack.
Mitigating compliance penalties
Documented cybersecurity practices also carry direct regulatory value. Under Section 13412 of the Health Information Technology for Economic and Clinical Health (HITECH) Act, the HHS Office for Civil Rights (OCR) must consider whether a covered entity or business associate had recognized security practices in place during the previous 12 months when making certain decisions about HIPAA Security Rule enforcement and audits.
The EU applies the same logic through a different mechanism. GDPR Article 32 requires security measures appropriate to the risk, and Article 83 makes the technical and organizational measures you had in place a factor in calculating a fine. NIS2 goes further: healthcare providers are classified as essential entities under Annex I, and the directive holds management bodies personally accountable for approving cybersecurity measures.
That consideration can affect fines, audit results, and other remedies after a violation. The HHS 405(d) program is one recognized source, so a framework also helps evidence that safeguards were in place before an incident.
Cleveroad provides healthcare software development services for solutions that account for HIPAA requirements and other safeguards from the architecture stage
The Main Healthcare Cybersecurity Frameworks Compared
Healthcare cybersecurity frameworks serve different purposes, so comparing them leads to the wrong choice. The practical task is to assign roles. One framework structures your security program. Another translates that structure into healthcare-specific practices. A third one you only need when someone outside your organization asks for proof.
NIST CSF 2.0
The NIST Cybersecurity Framework organizes cybersecurity into six functions: Govern, Identify, Protect, Detect, Respond, and Recover. NIST added Govern to CSF 2.0 in 2024 to strengthen focus on risk strategy, executive oversight, policies, roles, and supply-chain risk. NIST CSF 2.0 also maps well to HIPAA risk analysis. Govern and Identify help structure risk ownership, asset management, and risk assessment, which makes HIPAA security requirements easier to manage as a repeatable program.
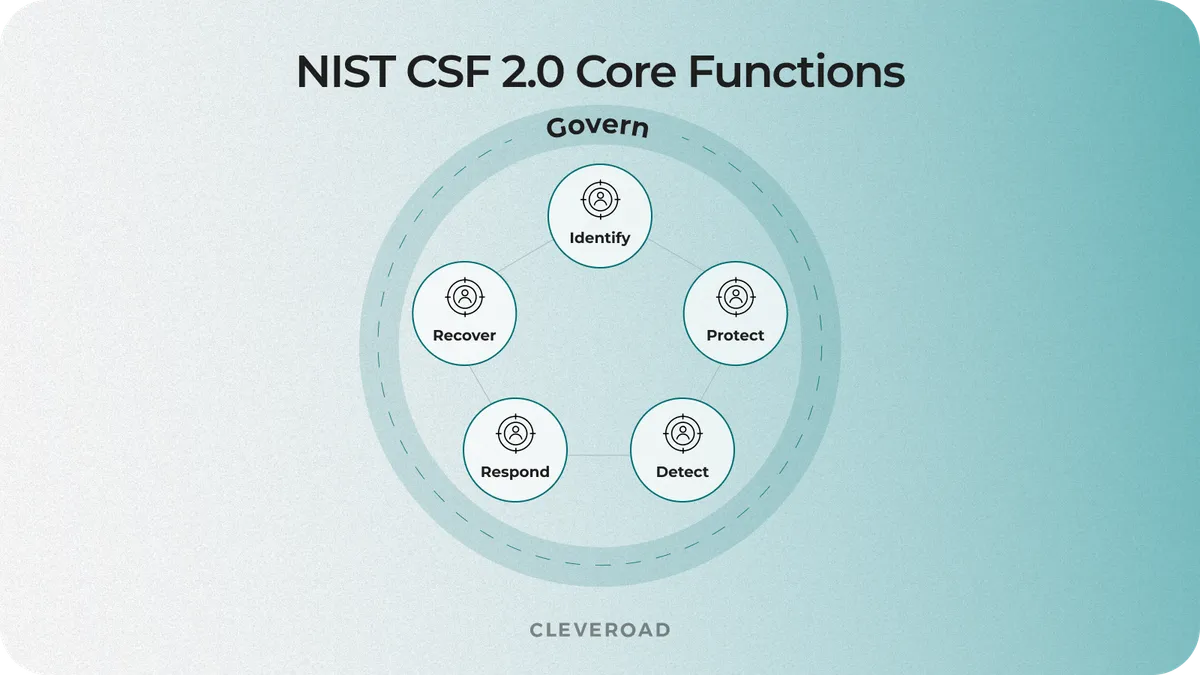
Healthcare cybersecurity frameworks stack
HHS 405(d) Health Industry Cybersecurity Practices
The HHS 405(d) Health Industry Cybersecurity Practices (HICP) translate cybersecurity principles into healthcare-specific actions. They cover practical controls for access, email security, data protection, vulnerabilities, and medical devices, with separate guidance for small and large healthcare organizations. HICP also maps to the NIST Cybersecurity Framework, so teams can connect healthcare-specific practices to a broader security program and prioritize controls based on their highest risks.
Canada has a close counterpart: the Canadian Center for Cyber Security publishes Baseline Cyber Security Controls for Small and Medium Organizations, the basis of the CyberSecure Canada certification, which plays the same role as HICP Technical Volume 1 plays for small US practices.
HITRUST CSF
The HITRUST CSF combines requirements from HIPAA, NIST, ISO/IEC 27001, PCI DSS, and other standards into one security and privacy framework. This helps healthcare organizations reduce duplicated compliance work across separate control sets. HITRUST also supports validated assessments and certifications, making it especially useful when payers, health systems, or enterprise customers require independent proof of security controls.
CIS Controls
The CIS Critical Security Controls provide prioritized technical safeguards for areas such as asset management, access control, vulnerability management, logging, and recovery. They are grouped into IG1, IG2, and IG3 based on an organization's security maturity and risk level. CIS Controls serve as a technical layer beneath NIST CSF 2.0, adding prescriptive safeguards to its broader governance and risk structure.
ISO/IEC 27001
ISO/IEC 27001 is an international standard for information security management systems (ISMS). ISO/IEC 27001:2022 helps organizations manage security risks and provides a certifiable framework recognized across markets. ISO 27799 extends ISO/IEC 27002 with health-sector guidance, so an ISMS built on 27001 can carry healthcare-specific controls without borrowing a US framework.
COBIT
COBIT is an IT governance framework that defines responsibilities, processes, and oversight. It works best alongside NIST CSF 2.0 or ISO/IEC 27001 for cybersecurity controls. A certified ISMS does not replace HIPAA. HHS still requires appropriate administrative and technical safeguards for ePHI, so ISO/IEC 27001 supports the security program while HIPAA remains the US regulatory obligation. The table below compares the six frameworks on what each one gives you, whether it comes with a certification path, and how much effort adoption typically takes.
| Framework | What it gives you | Certifiable | Best fit | Effort to adopt* |
|---|---|---|---|---|
NIST CSF 2.0 | Organization-wide structure for cybersecurity governance and risk management | No | US healthcare organizations that need a core security program | Medium |
HHS 405(d) HICP | Healthcare-specific practices linked to common sector threats | No | Small clinics and healthcare organizations that need a practical starting point | Low to medium |
HITRUST CSF | Harmonized controls plus independent assessment and assurance | Yes | Vendors and providers that need third-party proof for payers, health systems, or enterprise customers | High |
CIS Controls | Prioritized technical safeguards grouped into implementation levels | No | Teams that need a technical control layer under NIST or another governance framework | Low to medium |
ISO/IEC 27001 | International ISMS requirements and an accredited certification path | Yes | International organizations or healthcare companies that need management-system certification | High |
COBIT | Enterprise IT governance, objectives, responsibilities, and management processes | No organizational certification | Enterprises that need to connect cybersecurity with broader IT governance | Medium to high |
Effort is a relative estimate. Actual scope depends on organization size, existing controls, systems, risk profile, and whether formal certification or external validation is required. For a broader view of standards and safeguards, see our guide to healthcare data security.
How to Choose a Framework Based on Your Organization Type
To choose a framework, start with two questions: what is forcing the work, and who regulates you? A partner audit points to third-party assurance; an OCR or DPA finding points to documented remediation; a product launch points to a scalable program. Your jurisdiction then decides which framework fills each role.
If you are a small clinic or a first-time program
Start with HHS 405(d) HICP Technical Volume 1. HHS created this volume specifically for small healthcare organizations and recommends that smaller providers assess their existing practices, identify gaps, and build a remediation plan around the healthcare-specific safeguards in the guide.
Once those basics work consistently, use NIST CSF 2.0 to organize them into a broader risk management program. NIST supports organizations at different maturity levels through the CSF Core, Organizational Profiles, and Tiers, so you can expand the program without replacing the controls already in place.
For most first-time programs, HITRUST certification adds more assessment effort than you need at this stage. It becomes easier to justify when a payer, customer, or other relying party requires validated assurance.
Outside the US: small clinics in Canada can start with the Cyber Center Baseline Controls, while EU organizations can use ISO/IEC 27001 Annex A together with ISO 27799.
If you are a scaling provider or health system
Use NIST CSF 2.0 as the program structure and CIS Controls as the technical implementation layer. NIST helps you prioritize cybersecurity outcomes across governance, protection, detection, response, and recovery, while CIS provides detailed safeguards that map directly to CSF 2.0.
A practical readiness marker is whether you know what you need to protect and what risks require action. Start with an accurate asset inventory and a completed HIPAA risk analysis. Then verify that every identified risk has an owner and a corrective action, instead of leaving the assessment as a filed document. Both halves of that marker come from the frameworks themselves: CIS places enterprise asset inventory at the start of its control set, and HHS states that risk analysis should produce actions and feed an ongoing risk management process.
For EU providers: build NIS2 early warning, incident notification, and final reporting deadlines into your Respond procedures rather than treating them as part of the CSF profile itself.
If you sell software to health systems or public payers
Prioritize HITRUST when enterprise customers require independent security assurance. HITRUST assessments give healthcare buyers standardized, validated evidence that can reduce repetitive requests for evidence and support more efficient security and procurement reviews.
The compliance work also has reuse value. HITRUST CSF requirements map to the HIPAA Security Rule, so assessment evidence can support documentation of implemented controls, their effectiveness, and remediation plans. HITRUST notes, however, that a certification or assessment alone should not be treated as proof of complete HIPAA compliance.
For a healthcare software vendor, that reuse can justify the higher certification effort: the same control evidence supports customer assurance reviews and parts of your HIPAA documentation, rather than requiring separate evidence packages for every enterprise buyer.
In the EU, the gate is rarely HITRUST. Enterprise buyers ask for ISO/IEC 27001 certification, and if your software is a medical device, for MDR conformity - so the same budget buys you a different certificate depending on where your customers are.
Which framework fits depends on three inputs: your size, your security maturity, and who is asking for proof. The path below runs those inputs in order.
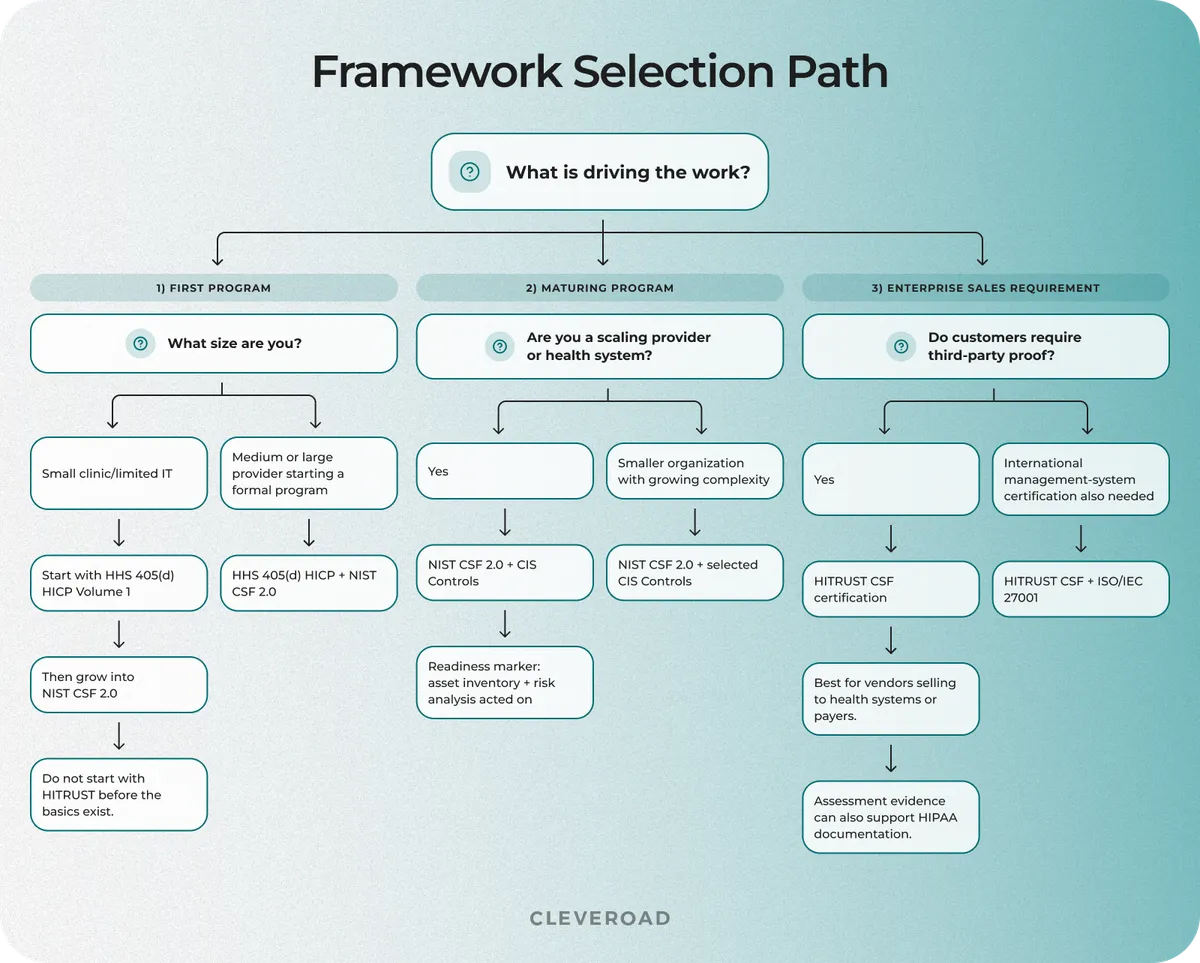
Framework selection path
How to Implement a Cybersecurity Framework
Framework implementation works as a continuous loop: define the target state, assess the current state, close the gaps, then measure the result and reassess. NIST CSF 2.0 follows the same logic through Organizational Profiles, gap analysis, action plans, and profile updates, and its Quick Start Guides break each stage into working templates.
The two steps teams tend to underestimate are the current-state assessment and the engineering work that follows it. A framework only improves security when identified gaps lead to changes in the software, infrastructure, access model, and recovery processes. The seven steps below run that loop end to end.
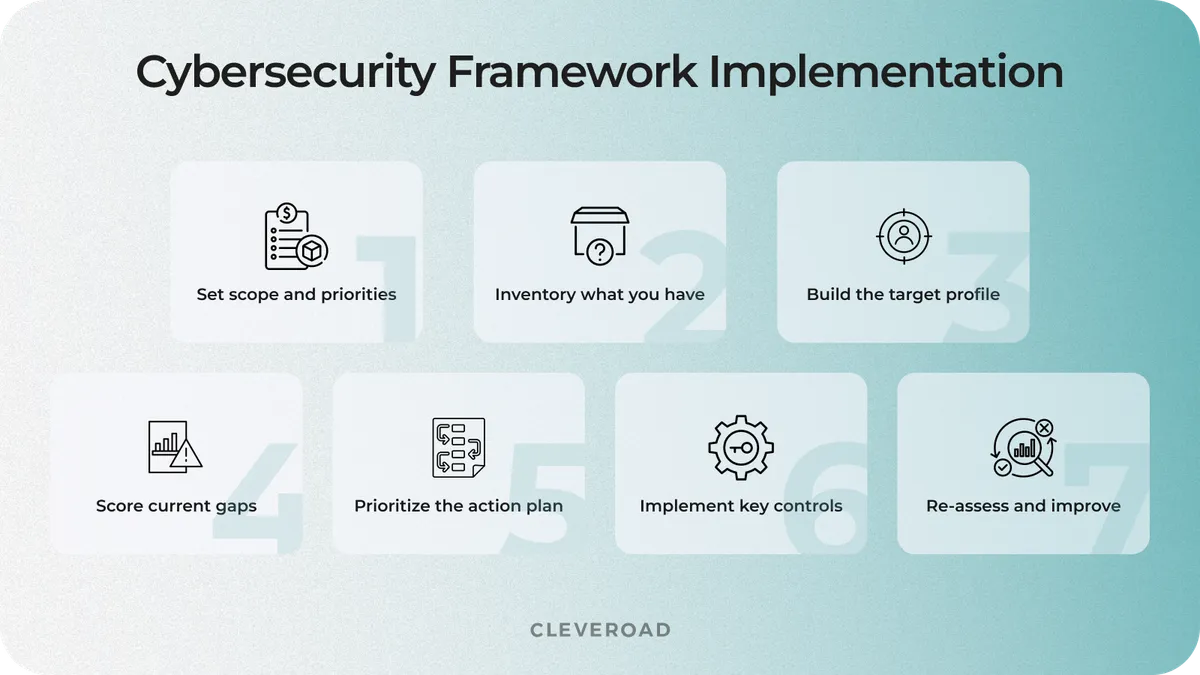
The implementation process, step by step
Step 1. Set scope and priorities
Define exactly which products, systems, protected health information (PHI) flows, departments, and third-party vendors the assessment covers. NIST CSF 2.0 recommends fixing the Profile scope before the assessment, including the technology assets, data assets, services, partners, and suppliers inside it.
Then keep that boundary stable. If teams keep adding systems, business units, and vendors, a bounded three-month assessment turns into a year-long program with no completion point.
Step 2. Inventory what you have
Inventory the systems, applications, data stores, connected medical devices, third parties that touch PHI, and the identities that can reach each resource. HHS notes that HIPAA risk analysis may include an inventory of systems used to access or store ePHI.
For EU organizations: GDPR Article 30 requires records of activities, so data and processing inventories become a compliance obligation rather than a recommended security practice.
An incomplete inventory undermines every downstream risk score. If your team does not know whether a legacy database, vendor integration, or unmanaged device exists, the assessment cannot measure the risk it creates.
Step 3. Build the target profile
Create a Target Profile that defines the cybersecurity outcomes your organization needs to achieve. Select the CSF Functions and Subcategories that belong in it. What makes an outcome relevant is your regulatory obligations, your threat exposure, and your risk tolerance.
NIST CSF 2.0 also lets you add your own outcomes when the Core does not cover a unique risk. Prioritize them, so the Profile reads as a roadmap rather than a checklist where every item weighs the same.
Step 4. Assess current state and score the gaps
Build a Current Profile and score how well each target outcome works today, reviewing the program by functional area: governance, infrastructure, applications, access management, vendors, incident response, and recovery. NIST suggests rating practices on a 1-to-5 scale, in percentages, or as red-yellow-green scores, then using a heat map to show leadership where risk concentrates.
Inherited systems and poorly documented code expose the largest engineering gaps at this stage. Security policies can look complete while the product still carries outdated dependencies, architectural bottlenecks, weak access controls, or undocumented data flows.
Cleveroad ran into exactly this gap on DECODE.ME, a teledermatology platform from Codex Labs. We joined as the third engineering partner, and the code audit surfaced architectural and backend defects that no policy document had recorded. The assessment output was not a score but a remediation list: which defects to fix, which parts of the infrastructure to rebuild around HIPAA requirements, and in what order.
We then fixed the critical backend issues and built a secure, HIPAA-compliant infrastructure for virtual doctor-patient consultations. Within five months, Cleveroad prepared a working DECODE.ME demo for the American Academy of Dermatology Innovation Meeting, where the platform attracted dozens of dermatologists who later joined it as users.
Watch Barbara Paldus, CEO at Codex Labs, share her experience working with Cleveroad:
Dr. Barbara Paldus, CEO at Codex Labs: Feedback on Cleveroad's Telemedicine Development Services
Step 5. Prioritize remediation and write the action plan
Convert each meaningful gap between the Current and Target Profiles into an action with an owner, priority, deadline, and budget. NIST recommends weighing mission drivers, benefits, risks, staffing, and funding rather than gap size alone.
Rank remediation by security risk and clinical impact, not by which fix looks easiest. If you accept a risk instead of fixing it, document the decision, its owner, the rationale, and why you rejected the alternatives.
Step 6. Implement the controls in the software and infrastructure
The action plan now becomes engineering work. Depending on the Target Profile and applicable requirements, common remediation tasks include:
- Role-based access control (RBAC) that restricts PHI and administrative functions by user responsibility.
- Audit logging that records access, security events, and changes to sensitive data.
- Encryption for sensitive data at rest and in transit.
- MFA for staff-facing and privileged systems.
- Network segmentation that separates connected medical devices and critical workloads from less trusted environments.
- Backup and recovery controls with tested restore procedures and defined recovery priorities.
These controls reach application architecture, cloud configuration, identity and access management (IAM), CI/CD, databases, networking, and monitoring. Cleveroad's DevOps services support the infrastructure and delivery changes, and our QA testing services validate that they work without breaking critical workflows.
Step 7. Measure, re-assess, and keep the loop running
Set metrics for each CSF function and re-score the Profile on a fixed cadence. One workable starting set:
- Govern: unresolved high-risk findings.
- Identify: asset inventory coverage.
- Protect: MFA coverage across staff and privileged accounts.
- Detect: time to detection.
- Respond: incident handling against defined response steps.
- Recover: successful restore tests.
NIST treats Profile updates as part of ongoing risk management. Changes in systems, vendors, threat exposure, or regulatory requirements should trigger an update to the Current Profile, Target Profile, or action plan rather than waiting for the next audit. That is what keeps the framework attached to the healthcare systems and PHI flows that actually change.
What Framework Adoption Requires From Your Software
This section covers what framework demand from the product itself, because the audit eventually reaches the architecture, not the policy that describes it.
Access control, audit logging, and encryption in the architecture
The controls from Step 6 only hold if the architecture enforces them rather than the policy describing them. Role-based access separates clinical, administrative, and privileged paths at the data layer, not in the UI. Audit records have to be tamper-resistant, which means write paths the application itself cannot rewrite. Encryption has to cover the storage layer and every transport hop, including internal service calls that never leave your cloud account.
We applied this approach when Cleveroad built a Clinic Management System for a US rehabilitation provider. The clinic was leaving a third-party electronic medical record (EMR) platform sold as a subscription service, which meant its PHI had to move into a new environment without breaking access rules along the way. A 16-person team migrated the existing patient data, deployed the custom platform on AWS with AES-256 encryption and role-based access controls, and integrated DoseSpot for e-prescriptions and Vonage for the telemedicine sessions.
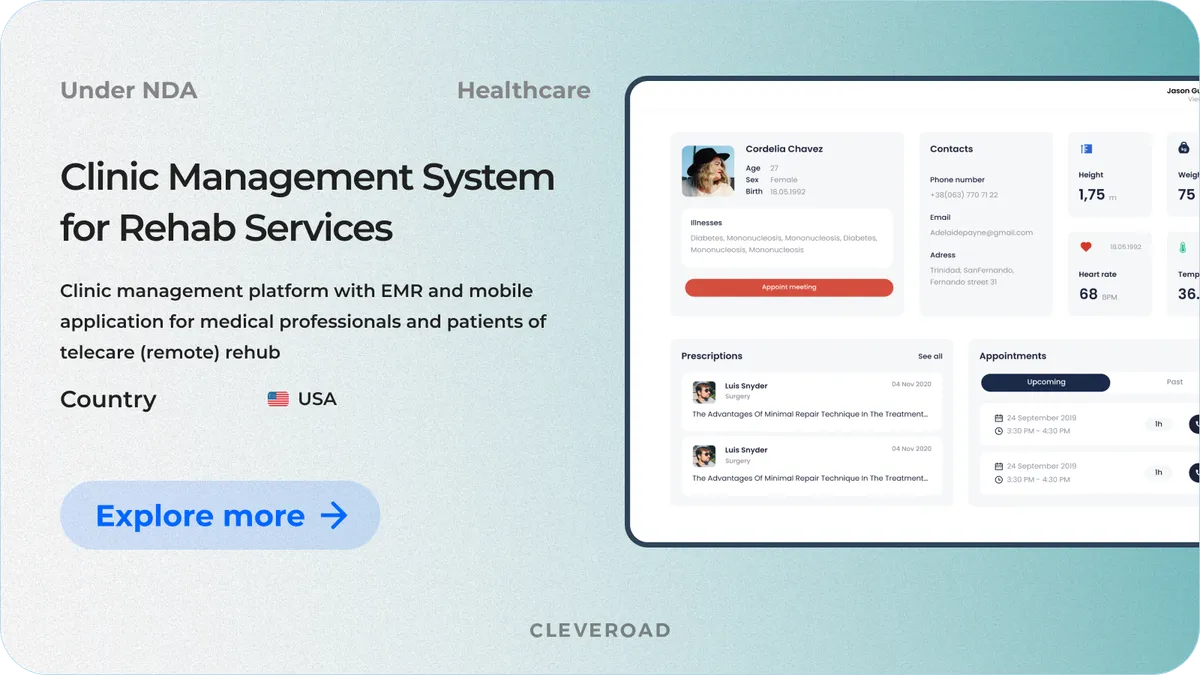
Interface of clinic management system
The infrastructure also uses multiple availability zones and standby database replicas to support high availability and recovery. These architectural measures map naturally to the Protect and Recover functions of a cybersecurity program because they protect PHI during normal use and help maintain access to critical services when infrastructure fails.
Connected devices and vendor dependencies
Connected healthcare products add another security boundary. Medical devices belong behind network segmentation, monitoring has to catch abnormal activity across devices, applications, and cloud infrastructure, and your documentation has to map every external vendor that stores, processes, or receives PHI. CSF 2.0 makes this explicit through the Govern GV.SC category: identify your technology suppliers, assess their criticality, define security requirements, and monitor supplier risk throughout the relationship.
For EU medical devices: MDR Annex I 17.2 requires protection against unauthorized access, while MDCG 2019-16 provides cybersecurity guidance across the device lifecycle. These requirements should sit alongside supplier-risk controls rather than remain a separate compliance track.
Cleveroad faced the device side of this problem while creating an Internet of Things (IoT) system for monitoring EKG and blood oxygen levels for a US medical device manufacturer. An 18-person team integrated ECG monitors and pulse oximeters with native mobile applications over Bluetooth and built offline storage so readings survive a dropped connection. The platform met Food and Drug Administration (FDA) 510(k) Medical Device Registration requirements, and 95% of user reviews rate the apps 4 or 5 stars.
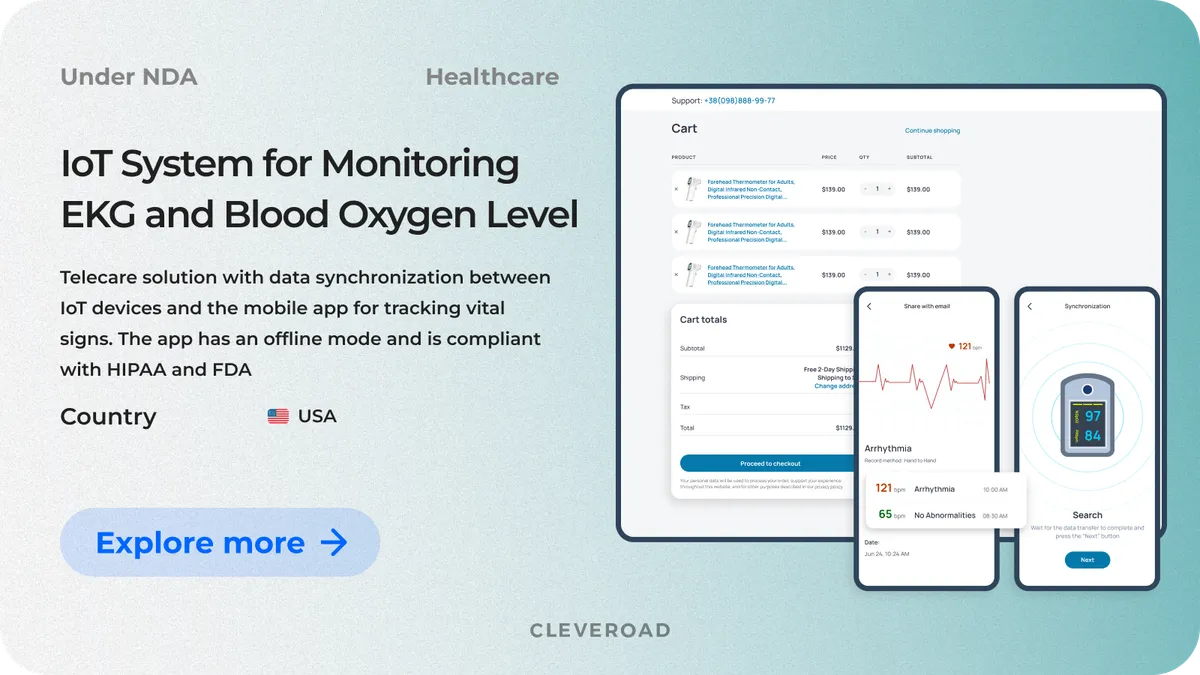
Interface of IoT based system of hydration monitoring
Legacy systems as the recurring blocker
Legacy software leaves framework gaps open because older systems often lack reliable patching paths, modern access controls, standardized integrations, or complete documentation. The same limits make it hard to add encryption, MFA, and monitoring without touching the existing architecture.
The decision comes down to modernizing or isolating each high-risk system. One that can take secure updates and integrations justifies modernization; one that cannot hold adequate controls needs network isolation, restricted access, replacement, or retirement. Our guide to legacy systems in healthcare covers how to assess each system on its own risk rather than applying one approach across the estate.
Cleveroad provides IT consulting services to assess your current systems and define the technical changes required to align software and infrastructure with the selected framework
Cleveroad's Expertise in Secure Healthcare Software Development
Cleveroad is a healthcare software development company with 15+ years of HealthTech experience. We build and modernize Electronic Health Record (EHR) and EMR systems, telemedicine platforms, remote patient monitoring solutions, and medical device software.
Cleveroad holds ISO 9001 certification for quality management and ISO/IEC 27001 certification for information security management. Depending on the project scope, our teams design healthcare solutions to meet applicable HIPAA and HITECH requirements, Health Level Seven (HL7) and Fast Healthcare Interoperability Resources (FHIR) interoperability standards, IEC 62304 for medical device software, and FDA requirements.
Depending on the project scope and target market, our teams design healthcare solutions to support applicable HIPAA, HITECH, GDPR, and EU MDR requirements, as well as HL7 and FHIR interoperability standards, IEC 62304 for medical device software, and FDA requirements.
Working with Cleveroad, you will receive the following benefits:
- Healthcare security expertise. We design PHI flows, access controls, encryption, and audit logging around the product's regulatory scope, and run the compliance review twice: at architecture design and before release.
- Cleveroad provides a 280-engineer core team plus a 2,100-specialist external talent network. Architects, analysts, engineers, QA, and DevOps come from our in-house team, while the external network helps us cover demand spikes without rotating people off your build.
- Existing-system assessment. We audit inherited code, find the security and architecture gaps, and produce a remediation roadmap before development continues.
- Cleveroad matches compliance measures to your product. We select safeguards based on the target market, software type, integrations, and medical-device classification.
Build secure healthcare software with Cleveroad
Get a healthcare-focused engineering team to assess your architecture and build software around the regulatory and security requirements that apply to your product
A healthcare cybersecurity framework structures how an organization identifies, manages, and reduces cyber risk. Frameworks such as NIST CSF 2.0 connect security goals with specific controls, responsibilities, and assessment processes.
The choice depends on your security goals. NIST CSF 2.0 serves as a broad foundation; HICP adds healthcare-specific practices, while HITRUST CSF is suited to organizations that need validated assurance or certification. Many organizations combine frameworks rather than rely on one.
Use an international baseline such as ISO/IEC 27001, then map regional requirements on top of it. In the US, align controls with HIPAA and frameworks such as NIST CSF 2.0; in the EU, account for GDPR, NIS2, and MDR where applicable.
This approach gives you one security management structure while keeping US and EU regulatory obligations separate.
NIST CSF 2.0 provides flexible, outcome-based guidance for managing cybersecurity risk and does not provide an official NIST certification. HITRUST CSF combines prescriptive requirements with standardized assessments and certification, making it more suitable for customers or partners who require validated assurance.
A scoped NIST CSF gap assessment for a single product typically takes 4-8 weeks. Remediation can take one to two quarters for access controls, logging, and similar security work, while major legacy-system changes can take more than a year.
HITRUST r2 certification can add around 9-12 months, including readiness work and the validated assessment. The final timeline depends on the initial security gaps, system complexity, and certification scope.
Evgeniy Altynpara is a CTO and member of the Forbes Councils’ community of tech professionals. He is an expert in software development and technological entrepreneurship and has 10+years of experience in digital transformation consulting in Healthcare, FinTech, Supply Chain and Logistics
Give us your impressions about this article
Give us your impressions about this article